Last updated: September 22, 2026
Healthcare compliance platforms cluster into four main feature categories, each with a different fit by organization type.
Knowing what the software does is only half the picture. The other half is understanding which framework your program must satisfy, because your platform has to produce evidence against that standard.
Most healthcare organizations describe their programs using a few common models. These models overlap, and each one highlights a different view of the same obligations.
OIG's 2023 General Compliance Program Guidance updated the element names, making risk assessment part of a named element (Element 6: Risk Assessment, Auditing, and Monitoring) rather than an implied prerequisite. Programs built against older seven-element lists may not map cleanly to current OIG expectations.
The four-pillar model restates these same duties in a simpler structure that focuses on ownership and oversight.
Another way to view the same obligations groups them by risk area instead of by governance structure.
Cybersecurity frameworks such as NIST CSF and control catalogs such as NIST SP 800-53 sit alongside these models and shape how organizations manage technical safeguards.
The NIST Cybersecurity Framework (CSF) was originally designed to help critical infrastructure organizations manage cybersecurity risks, but its flexible, risk-based approach has driven widespread adoption across industries. Where NIST CSF provides the organizing framework, NIST SP 800-53 supplies the detailed control catalog. NIST SP 800-53 is a U.S. federal catalog of security and privacy controls implemented as part of an organization-wide risk management process. It is mandatory for federal agencies and contractors under FISMA, and healthcare organizations subject to HIPAA often adopt it voluntarily by mapping its controls to HIPAA Security Rule requirements. NIST does not operate a certification program for NIST CSF or SP 800-53.
Many healthcare organizations also align with ISO 27001 and HITRUST to satisfy partner and payer expectations.
ISO/IEC 27001 is an internationally recognized management-system standard. It requires organizations to build and operate an Information Security Management System (ISMS), and accredited bodies can certify that system. NIST CSF, by contrast, is flexible and outcome-oriented and does not produce a formal certification. Many healthcare organizations map to both, using NIST to organize their security program and ISO 27001 to provide third-party assurance to partners and customers. HITRUST CSF harmonizes HIPAA, NIST, ISO 27001, and SOC 2 into a single certifiable control framework, and healthcare organizations, health plans, and business associates increasingly require HITRUST certification as a vendor qualification criterion.
Get a Compliance Workflow Walkthrough
Smaller practices usually operate with limited staff and no dedicated compliance officer, so responsibility often falls to an office manager. Primary risks include HIPAA Privacy and Security Rule violations and OSHA compliance. Small practices rarely have a dedicated compliance function, and the responsibility lands on an office manager or practice administrator with no formal training.
HIPAA-focused tools with guided risk assessments, policy templates, and automated training delivery fit this tier best. Pricing details for this category appear in the cost FAQ below. Look for platforms that a non-expert can run without dedicated compliance staff.
Multi-site cardiology groups often manage different policy versions, inconsistent training completion, and complex credentialing across providers and locations. The recurring compliance failure in health systems and hospitals is that each facility runs its own policy set, so nobody can answer which version of a rule any given site is operating under.
These organizations benefit from workforce training platforms combined with policy management that provides cross-location visibility. The priority is keeping every site on the same current policy set and tracking training completion by location and role. Pricing guidance for this tier appears in the cost FAQ.
Integrated health systems manage enterprise-scale policy governance, complex vendor oversight, multi-framework requirements such as HIPAA, HITRUST, and SOC 2, and board-level reporting expectations.
Enterprise GRC systems work best here because they map controls across multiple frameworks, automate evidence collection, and provide real-time program health dashboards. Enterprise GRC platforms built for large organizations take 6 to 12 months to implement.
Healthcare SaaS vendors carry business associate obligations under HIPAA and often face SOC 2 attestation and HITRUST certification requirements from enterprise buyers.
SOC 2 plus HIPAA platforms that support continuous monitoring, BAA management, and evidence reuse across frameworks fit these organizations. Cloud service providers engaged to create, receive, maintain, or transmit electronic PHI on behalf of a covered entity or business associate are business associates subject to BAA requirements.
HIPAA governs privacy and security of protected health information under 45 CFR parts 160 and 164. The Privacy Rule, Security Rule, and Breach Notification Rule each create specific expectations for privacy practices, safeguards for electronic PHI, and breach response obligations. OCR ended 2025 with 21 HIPAA settlements and civil monetary penalties, the second-highest annual total in the program's history.
OSHA regulations applicable to healthcare cover bloodborne pathogens, respiratory protection, hazardous substances, and personal protective equipment. These requirements matter most in hospitals, ambulatory settings, and laboratories.
CMS enforces billing compliance and coding accuracy. Practices billing federal programs must ensure documentation supports every claim, particularly for complex remote monitoring codes.
HITRUST harmonizes HIPAA, NIST, ISO 27001, and SOC 2 into a single certifiable control framework. A single screenshot of an encryption configuration can satisfy HIPAA Security Rule 164.312, a HITRUST control, and SOC 2 CC6.1 simultaneously. This evidence reuse explains why multi-framework compliance has become the norm.
Software supports this evidence reuse but still relies on program ownership, a compliance officer, and staff training.
With this regulatory context in place, cardiology and EP practices can evaluate how general tools fall short for cardiac device workflows.
General healthcare compliance software covers policy management, training, risk assessment, and credentialing. Cardiology and EP practices that manage cardiac implantable electronic devices (CIEDs) also carry a highly audit-exposed workflow: remote monitoring documentation and CPT capture.
Practices implanting devices from Medtronic, Boston Scientific, Abbott, and Biotronik must log into separate, non-interoperable portals to retrieve patient data. This fragmentation creates data silos, manual transcription errors, and audit risk because documentation lives in multiple systems instead of a single record. High dismissal rates in CIED monitoring are structural features of safety-first remote monitoring, with most OEM-generated alerts being nonactionable. That volume makes manual, portal-by-portal workflows operationally unsustainable.
Pacemakers and ICDs on a 90-day cycle use:
Physiologic monitors and loop recorders on a 30-day cycle use device-specific codes:
Each of 93297 and 93298 is billable once per 30-day monitoring period and can be billed global, with modifier -26 (professional component), or with modifier -TC (technical component). These are device-specific codes. Code 93297 applies to implantable cardiovascular physiologic monitors and 93298 applies to subcutaneous cardiac rhythm monitors and loop recorders. They do not form a professional and technical pair.
For remote physiologic monitoring of heart failure and hypertension patients, 99454 covers the monthly device supply and data transmission when the patient has 16 or more days of data within a 30-day period.
The six most common CPT 93298 denial causes are wrong code for the device, reporting before 30 days, more than one claim per interval, unsigned or undated report, modifier mismatch, and bundling with in-person interrogation codes without checking NCCI edits. Automated documentation, device-specific CPT pairing, and a full audit trail help practices avoid these failure patterns.
Rhythm360 by RhythmScience is a vendor-neutral, HIPAA-compliant, cloud-based platform built specifically for cardiac RPM and CIED workflows. It consolidates all CIED and RPM data into a single source of truth. Because the platform normalizes data from all major manufacturers, it can automate CPT capture and documentation for device-specific codes including 93294–93298 and 99454. University of Chicago Medicine reviewed more than 73,000 reports annually through Rhythm360 in calendar year 2025, averaging more than 18,000 reports per quarter. That volume demonstrates the platform's scalability for high-volume CIED monitoring programs.
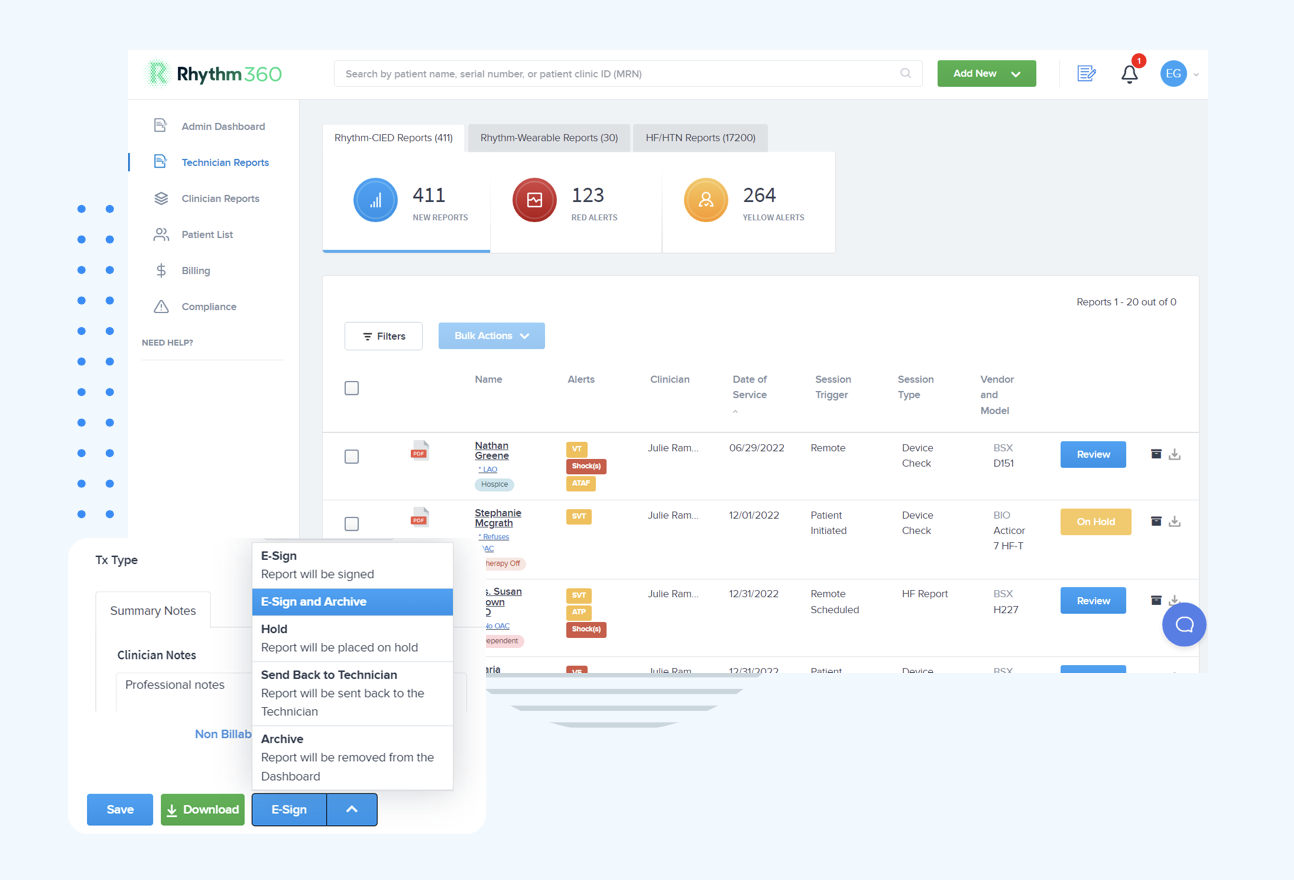
Rhythm360 provides bi-directional EHR integration with Epic, Cerner, Athenahealth, eClinicalWorks, and Greenway Health. Practices using the platform have seen up to a 300% increase in revenue capture and up to an 80% reduction in critical alert response times. The capabilities below show how the platform supports both compliance and revenue integrity.
See How Rhythm360 Handles CIED Data
This checklist helps teams compare vendors and confirm that a platform supports both general compliance needs and cardiac device workflows.
Teams can use the answers to narrow vendors to a short list and then request targeted demos focused on cardiac workflows.
Healthcare compliance software supports and documents compliance activities, but it does not make a practice compliant on its own. Program ownership, a designated compliance officer, and staff training remain required. Software provides the infrastructure for tracking, evidence collection, and audit readiness. The OIG is explicit that compliance programs must be scaled and designed according to an organization's size, structure, and areas of risk.
The most effective platform for a cardiology practice combines general compliance capabilities with cardiac RPM and CIED data handling. General compliance platforms that focus on policy management, LMS, and risk tools rarely address the remote monitoring documentation and CPT capture workflow that cardiology and EP practices require. Rhythm360 is purpose-built for this problem, consolidating device data from major manufacturers, automating CPT documentation for 93294–93298 and 99454, and providing audit-ready reporting for cardiac device workflows. Other platforms in the cardiac remote monitoring space include Murj, Implicity, Rhythm Management Group, and Octagos.
Pricing varies by organization size and modules. Self-serve HIPAA tools often start around $169 per month. Small practices typically pay between $2,000 and $6,000 per year for a full program platform. Mid-market and multi-location organizations more often fall between $10,000 and $40,000. Enterprise GRC systems used by health systems can run significantly higher, with implementation timelines of six to twelve months. Rhythm360 uses a SaaS-based pricing model that scales with clinic size and platform usage.
Compliance software can support RPM billing when the platform is designed for cardiac device workflows. Automated CPT capture and documentation for codes such as 93294–93298 and 99454 can reduce denials and help practices capture previously lost revenue. The key requirements are device-specific CPT pairing, because 93297 applies to implantable cardiovascular physiologic monitors and 93298 applies to subcutaneous cardiac rhythm monitors, and a complete audit trail that survives payer scrutiny. This functionality requires a platform built specifically for cardiac device data workflows.
NIST CSF is a voluntary, U.S.-origin framework that helps organizations organize and improve their security program through self-assessment. It produces no formal certification. ISO 27001 is an internationally recognized standard that requires organizations to build and maintain an Information Security Management System (ISMS) and undergo external audits to earn a three-year certificate. For healthcare organizations, NIST CSF is useful for structuring internal risk management, while ISO 27001 provides third-party assurance that enterprise partners and procurement processes recognize. Many healthcare organizations use both, and HITRUST CSF harmonizes HIPAA, NIST, ISO 27001, and SOC 2 into a single certifiable framework that an increasing number of health plans and business associates require as a vendor qualification criterion.
Cardiology practices can assemble point solutions, such as one tool for HIPAA training, another for policy management, and another for credentialing. General healthcare compliance software supports the program infrastructure that every healthcare organization needs. Cardiology and EP practices that manage CIEDs and RPM patients also need reliable support for remote monitoring documentation and CPT capture, which general compliance platforms typically do not provide.
Rhythm360 supports the broader compliance program and addresses cardiac RPM documentation in the same environment. It consolidates device data, automates CPT pairing, and delivers audit-ready reporting in a single HIPAA-compliant, vendor-neutral platform.
Talk to Our Team About Your Program